4 Server Configuration
The host backend provides the platform with the ability to connect to the server.
In the host backend, each organization can manage a server configuration. After the connection is completed, the platform can interact with the host backend through specific interfaces.
Thus, functions such as obtaining the game list and exposing the game login interface are implemented.
4.1 Server Token
The server token is an identity identifier provided by the host backend for the platform.
The platform can use this token to access the server interface of the host backend; it can also use this token to verify the identity of requests from the host backend.
Please keep the server token properly. If you find that the server token has been leaked, please reset it in the host backend as soon as possible.
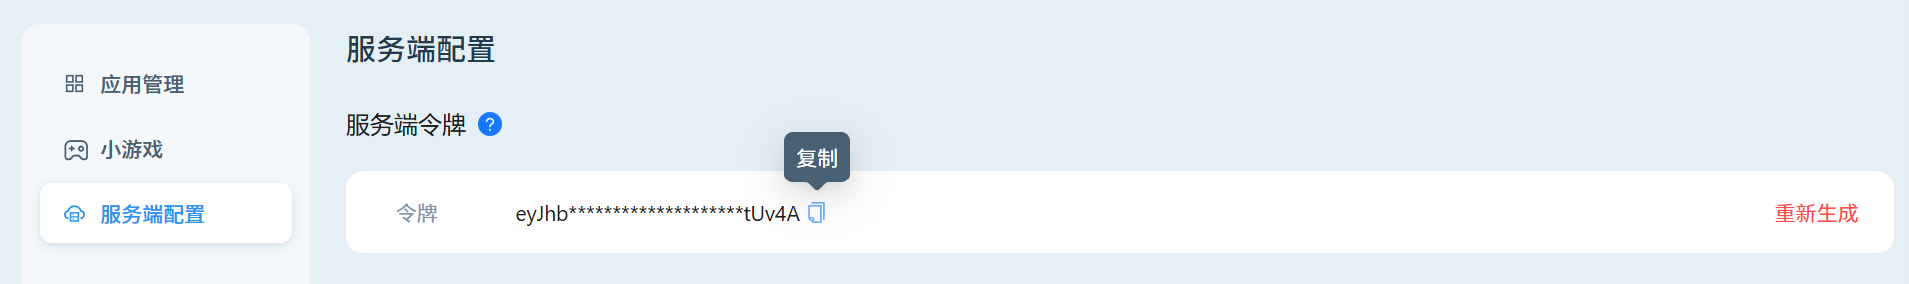
Please refer to the instructions in Server Token Integration Specification Use a token to obtain a list of minigames to use the server token.
4.2 Platform Access URL
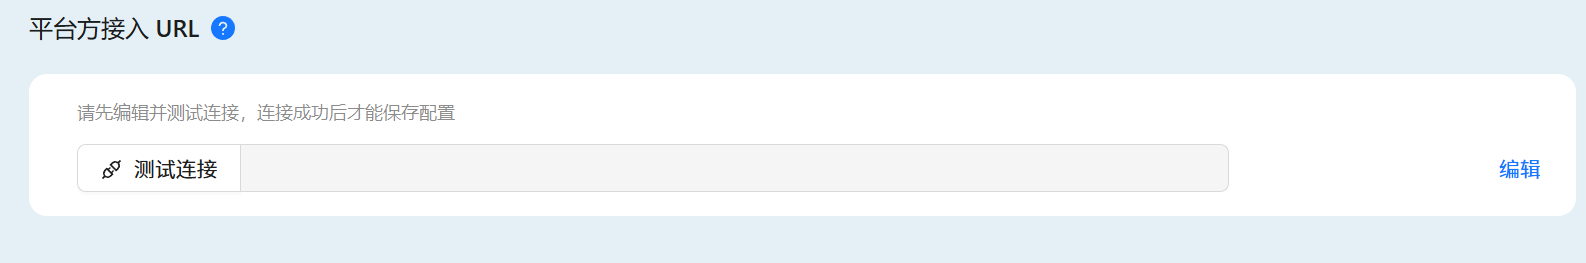
Here defines the implementation guidelines for the platform's APIs. If you are a game developer, please refer to
Section 2.1.2 - jscode2sessionfor integration.
After implementing specific interfaces on the server side, the platform can expose capabilities such as user login from the unified interface of the host backend to the game side for integration.
ping
It is used to test the network connectivity between the host backend and the platform. Only after the connectivity verification is successful can the URL be configured into the host backend.
Example of request:
Response Example:
Complete the implementation of the server-side API, and then configure the platform's access URL in the host backend.
jscode2session
Provide the platform's login capability. The host backend will pass the user's login credential (code) to the platform, and the platform needs to return the user's login information based on this credential.
The host backend will map the uid returned by the platform to the openid and unionid available on the game side, based on the context of the request, and forward the session_key to the game side as a login credential.
Example of request:
Request Parameter Description:
| Parameter | Description |
|---|---|
| js_code | Platform login credentials |
| Authorization | Server token, formatted as Bearer {service_token} |
Response Example:
Response field description:
| Field | Description |
|---|---|
| uid | Unique user identifier returned by the platform |
| session_key | session_key returned by the platform |
| errcode | Error code, 0 indicates success |
| errmsg | Error Message |
4.3 Payment Signature Secret
The payment signature key is an important credential for ensuring game payment security. After a user completes a game payment on the platform, the platform needs to use this key to digitally sign the payment result. The host backend will only forward the payment success notification to the game server after verifying the legitimacy of the signature, thereby ensuring the data integrity and security of the entire payment process.
Please properly safeguard the payment signature key and avoid leaks. If you suspect that the key may have been compromised, please immediately regenerate a new payment signature key in the host backend.
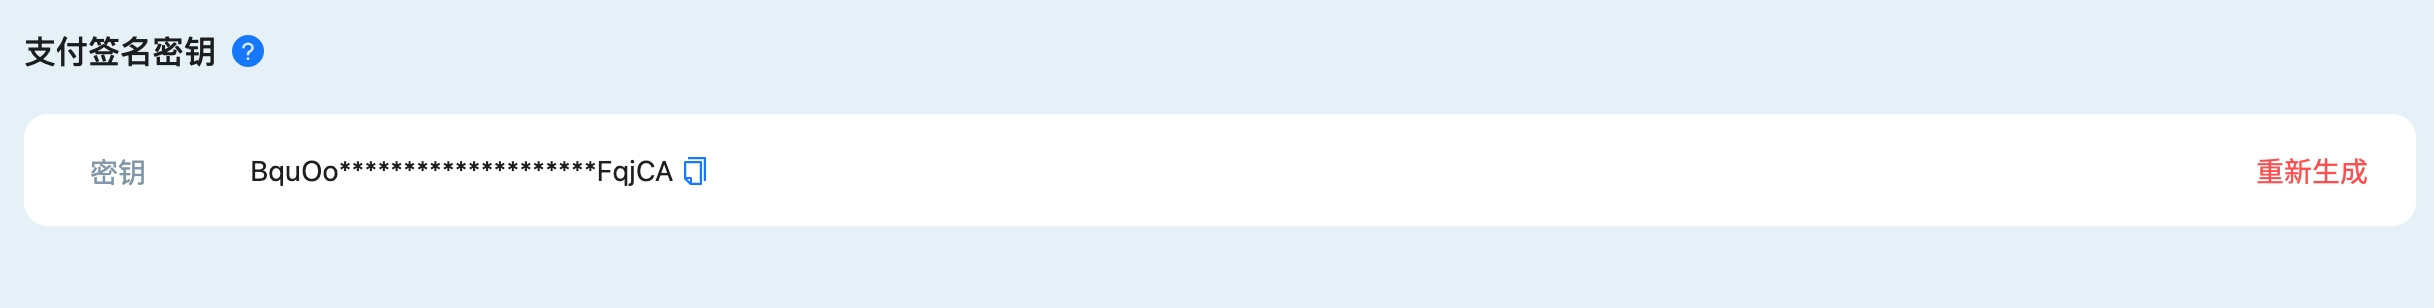
Please follow the instructions in Payment Signature Verification to implement the payment result notification interface, ensuring that you can properly handle payment notifications with signature verification.